
Deprovisioning in identity and access management (IAM) means removing an identity's access once the business requirement or authorization for that access ends, whether that's because an employee leaves, a contractor's project wraps up, or a role no longer needs a specific permission.
It's a core part of the identity lifecycle, which spans creation, modification, and eventual removal of access, and a critical capability within Identity Governance and Administration (IGA), where policies and controls govern how organizations manage access according to roles, business requirements, and lifecycle events. One of the clearest ways to see deprovisioning in context is through the Joiner-Mover-Leaver (JML) framework, where it marks the final, and often most overlooked, stage.
Done well, deprovisioning closes the gap that attackers love most: dormant accounts with live access. Let’s look at the importance of deprovisioning, how it works, its best practices, and more in this article.
Why Is Deprovisioning Important?
User access can change frequently. Employees move between departments, contractors complete projects, temporary privileges expire, and users stop working with particular applications. If those changes are not reflected across connected systems, unnecessary access can remain active.
Prevent Unauthorized Access
When an employee or contractor leaves, their access should be removed from the systems they no longer need. Deprovisioning can revoke access to applications, cloud services, VPNs, collaboration platforms, and other resources.
This reduces the chance of a former user continuing to access organizational resources after their authorization has ended, making user lifecycle management simpler.
Remove Orphaned Accounts
An orphaned account is an account that remains active without a valid owner or current business need.
These accounts can result from incomplete offboarding, manually created application accounts, or disconnected identity systems. Automated deprovisioning helps reduce the number of accounts that remain active after a user's lifecycle status changes.
Reduce Security Risk
Unnecessary access can increase exposure to credential misuse, privilege abuse, insider threats, and unauthorized access to sensitive data.
Deprovisioning supports least privilege by removing access when the underlying business need no longer exists.
Support Compliance and Audits
A controlled deprovisioning process creates records of access changes, including when access was revoked, which systems were affected, and whether the operation succeeded.
These records can support:
- Access reviews
- Audit investigations
- Internal access controls
- Employee offboarding records
- Evidence of lifecycle management
Reduce Unused License Costs
Removing inactive application accounts can also help organizations reclaim licenses that are no longer required.
For SaaS applications, this can reduce unnecessary license assignments while keeping application directories cleaner.
How Does Deprovisioning Work?
A typical deprovisioning workflow can follow this sequence:
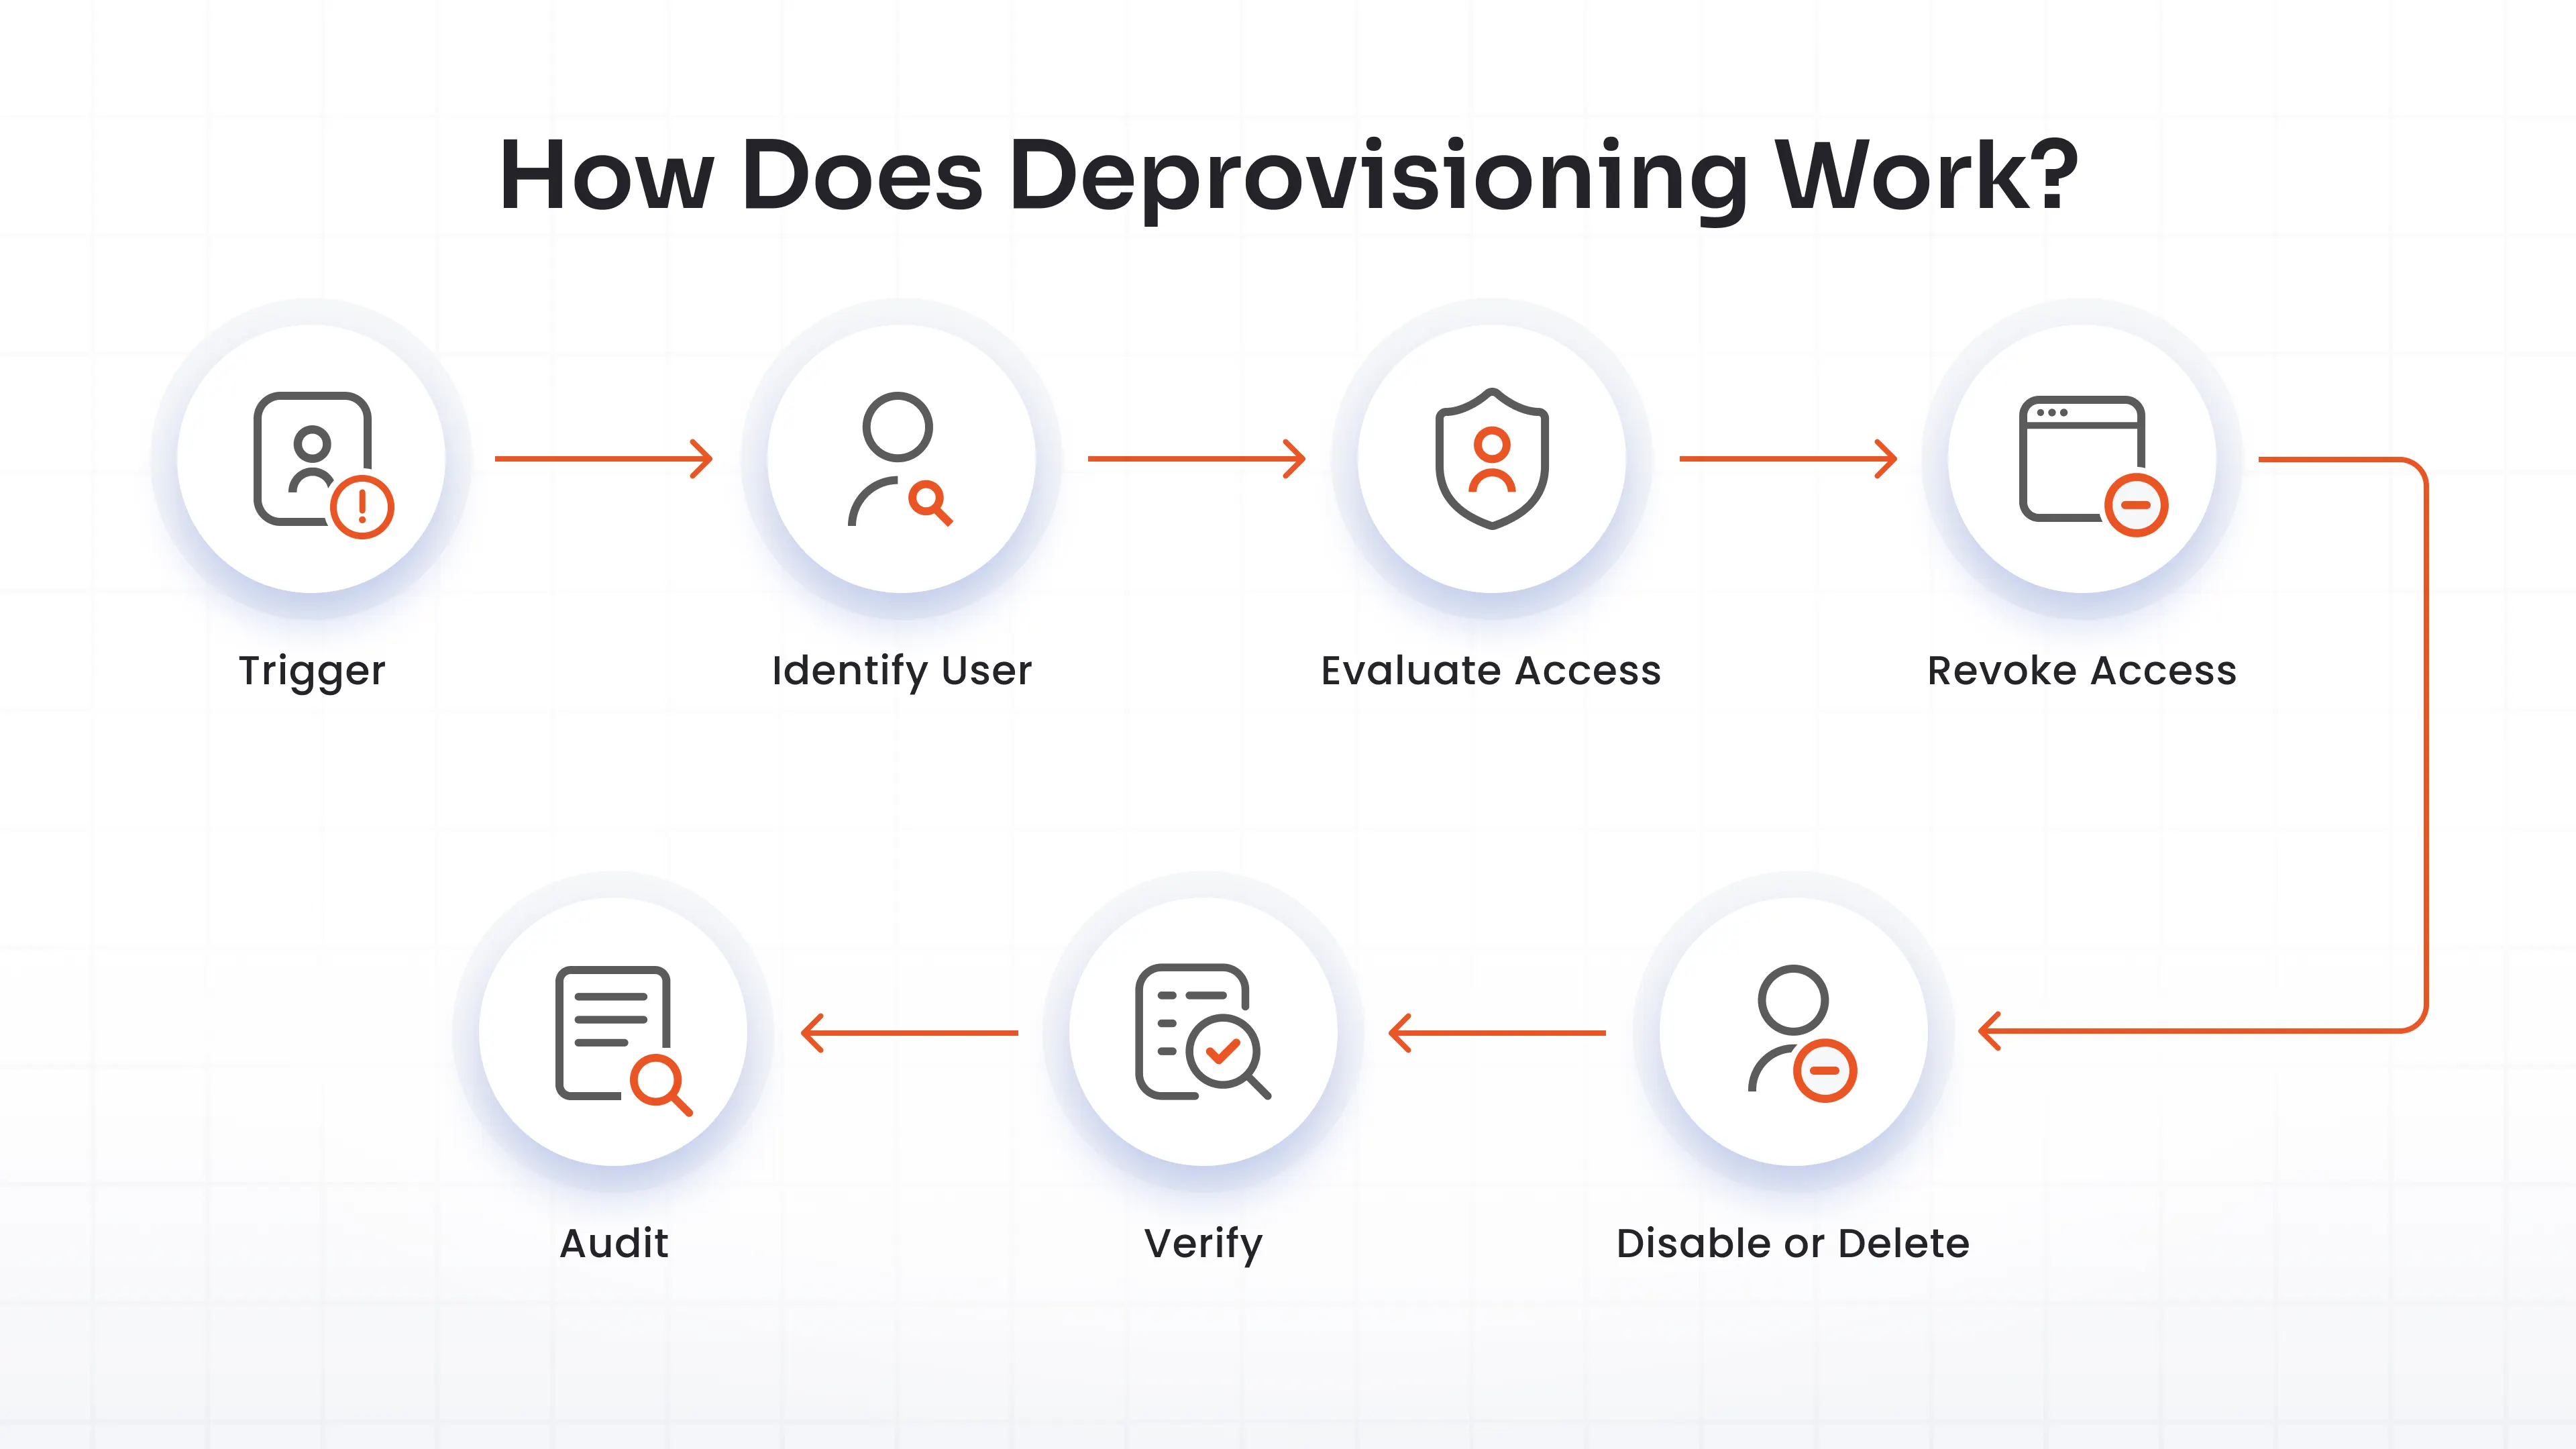
The exact workflow depends on the organization's IAM architecture, access policies, applications, and retention requirements.
Step 1: Trigger the Lifecycle Event
The process starts when an event indicates that a user's access needs to change. Common triggers include:
- Employee termination
- Department or role change
- Contractor engagement ending
- Temporary access expiration
- Removal of application access
- Security incidents requiring immediate revocation
An HR system is often used as an authoritative source for employee lifecycle events. For example, changing an employee's status to inactive can initiate downstream access changes.
Step 2: Identify the User and Their Access
The IAM system identifies the user's accounts and resources across the environment. This can include:
- Applications
- Groups
- Roles
- Permissions
- SSO assignments
- SaaS accounts
- Cloud resources
- Active sessions
- Privileged accounts
- Assigned licenses
The objective is to determine where the user has access, rather than simply disabling one primary account.
Step 3: Evaluate What Access Must Be Removed
Not every lifecycle event requires complete account removal. For example, when an employee changes departments, their identity remains active, but access associated with their previous role may need to be removed. Access can be evaluated using:
- User attributes
- Role assignments
- RBAC policies
- Application requirements
- Access expiration rules
- Organizational policies
This makes deprovisioning an important part of access provisioning and deprovisioning throughout the identity lifecycle.
Step 4: Revoke Access
The workflow removes the access identified during the evaluation stage. Depending on the environment, this can include:
- Removing application assignments
- Removing group memberships
- Revoking permissions
- Invalidating active sessions
- Removing SSO access
- Revoking credentials
- Removing privileged access
Step 5: Disable or Delete Accounts
Deprovisioning does not always mean permanently deleting an account. An organization may disable the account, remove its access, archive associated information, or delete the account depending on its security, operational, and retention policies.
For example, an employee's account may be disabled when they leave, while certain records are retained for business or regulatory requirements.
Step 6: Verify and Record the Result
The final step is confirming that the expected access changes were completed. Organizations should verify:
- Connected applications were updated
- Access was successfully revoked
- Sessions or credentials were invalidated where required
- Licenses were reclaimed where applicable
- Failed operations were identified
- Audit records were created
Verification matters because a successful status change in one identity system does not necessarily mean every connected application has removed the user's access.
How Does SCIM Support Deprovisioning?
SCIM, or System for Cross-domain Identity Management, is a standard for exchanging identity information between systems. It can automate user and group lifecycle operations between an identity provider and compatible applications.
SCIM can support operations such as:
- Creating users
- Updating user attributes
- Deactivating users
- Removing users
- Managing groups
- Synchronizing user information
A typical automated flow looks like this:
HR System → IAM/IdP → SCIM → SaaS Application
For example:
HR status changes to inactive
↓
IAM detects the lifecycle event
↓
SCIM sends the user update
↓
Application deactivates the account
↓
Access is revoked
This approach reduces the need for administrators to manually update each connected application. It also helps create a more consistent user provisioning and deprovisioning process across SaaS environments.
The exact action depends on the application's SCIM implementation. Some applications may deactivate a user, while others may support deletion or other lifecycle operations.
Deprovisioning Best Practices
Effective deprovisioning requires more than disabling a user's primary account. The process should account for the user's complete access footprint.
Use an Authoritative Source
Use an HR system, directory, or another trusted source to initiate lifecycle changes. For example, an employee's termination status can trigger automated workflows instead of requiring separate requests to every application owner.
Automate Access Removal
Manual deprovisioning becomes difficult to maintain as organizations add more users and applications. Automated workflows or HR IT provisioning can connect lifecycle events to predefined access changes, making the process faster and more consistent.
Deprovision Across All Applications
Removing access from the primary directory is only one part of the process. Include resources such as:
- SaaS applications
- Cloud platforms
- Databases
- VPNs
- Collaboration tools
- SSO applications
- Development environments
- Privileged systems
Include Contractors and Third Parties
Contractors, vendors, partners, and temporary workers can also accumulate access. Their accounts should have defined owners, access periods, and expiration conditions so that access is automatically removed when the engagement ends.
Maintain Audit Logs
Record important details for each deprovisioning event:
- User affected
- Date and time
- Triggering event
- Applications affected
- Access removed
- Success or failure status
These records make it easier to investigate access issues and demonstrate that lifecycle controls are being followed.
Verify Access Removal
Do not assume that changing a user's status automatically removes every downstream entitlement. Check provisioning logs, application status, workflow results, and access records to confirm that the expected changes occurred.
Run Regular Access Reviews
Automation reduces manual work, but regular access reviews can still identify accounts or permissions that were missed. Reviews are particularly useful for finding:
- Orphaned accounts
- Excessive permissions
- Unused application access
- Dormant accounts
- Unexpected group memberships
Deprovisioning Use Cases
Deprovisioning in automated user provisioning applies to several identity lifecycle events, not just employee departures.
Employee Offboarding
When an employee leaves, deprovisioning can revoke access across applications, directories, cloud systems, collaboration platforms, and other resources.
Role or Department Change
When a user moves to another role, access associated with their previous position can be removed while new role-based access is assigned.
This supports the Mover stage of JML and helps prevent privilege accumulation.
Contractor Offboarding
When a contractor's engagement ends, their temporary access can be revoked based on the contract end date or another defined lifecycle event.
Temporary Access Expiration
Access granted for a project or specific period can be configured with an expiration condition. When the period ends, the associated access can be removed automatically.
Security Incident
If an identity is compromised or presents an immediate security concern, access can be revoked across connected systems as part of the incident response process.
Application Access Removal
A user may remain employed but no longer require a specific application. In this case, the application entitlement can be removed without deleting the user's identity.
Turn Lifecycle Events Into Controlled Access Changes
Deprovisioning is a fundamental part of Identity Lifecycle Management. It ensures that user access changes when the underlying business requirement changes, whether that means an employee leaving, a role changing, a contract ending, or application access expiring.
A reliable approach combines an authoritative HR system or directory, defined lifecycle policies, automated deprovisioning workflows, application integrations, access reviews, and audit records.
When these controls work together, organizations can keep access aligned with current roles and business requirements while reducing orphaned accounts, unnecessary permissions, and manual access management.
FAQs
What is the difference between deprovisioning and deactivation?
Deactivation generally disables an account, while deprovisioning covers the broader process of removing an identity's access from relevant systems. Deprovisioning can include account deactivation, permission removal, group membership changes, session revocation, or deletion, depending on policy.
What's the difference between deprovisioning and decommissioning?
Deprovisioning removes a user's access or identity from systems, while decommissioning retires an entire system, application, service, or resource.
For example, when an employee leaves, their application accounts may be deprovisioned. If an organization permanently retires that application, the application itself may be decommissioned.
In simple terms:
- Deprovisioning: Remove a user's access.
- Decommissioning: Retire the technology or resource itself.
What happens if a user is not deprovisioned?
The user may retain access to applications, data, groups, cloud resources, or other systems they no longer need. This can result in orphaned accounts, excessive permissions, unnecessary license assignments, and increased security exposure.
What is automated deprovisioning?
Automated deprovisioning uses predefined rules, integrations, and lifecycle events to remove access without requiring administrators to manually update every connected system.
It can use IAM platforms, APIs, directories, SCIM, and application integrations to propagate access changes.
How does deprovisioning support Joiner-Mover-Leaver processes?
Deprovisioning supports both the Mover and Leaver stages of JML. During a role change, unnecessary access can be removed. When a user leaves, their access can be revoked across connected systems.
Can deprovisioning remove access from multiple applications?
Yes. When an IAM or identity provisioning system is integrated with multiple applications, a single lifecycle event can trigger access changes across those systems. SCIM can also automate user and group lifecycle operations for compatible applications.
Leave a Comment